Independent advisory · India & beyond

Build trust into
the way you work.

Practical information security, ISO 27001 and ISO 9001 consulting, audit and training for organisations ready to grow with confidence.

25+ years building information security systems
across organisations of every size
ISO/IEC 27001 certified auditorISO 9001 certified auditorFormer CISOTrainer & mentor
01 Our point of view

Good governance should
move business forward.

Security and quality systems work best when they fit the realities of your business. We help you make them useful: clear enough to act on, rigorous enough to stand up to scrutiny, and built to last.

↘
02 What we do

Expertise that meets
you where you are.

From first assessment to ongoing assurance, get senior-led support shaped around your risks, teams and goals.

02 / Audit

Internal Audits (ISO 27001 & ISO 9001)

Independent, evidence-based internal audits that satisfy the standard and genuinely improve the system.

  • Audit programme and schedule planning
  • Process, control and clause-level audits with sampled evidence
  • Clear findings: nonconformities, observations and opportunities for improvement
Learn more
03 / Third party

Supplier & Third-Party Audit Support

Assess and assure vendors, or prepare for the customer audits you receive.

  • Supplier risk tiering and assessment questionnaires
  • On-site or remote third-party security and quality audits
  • Review of supplier certifications, scope and Statements of Applicability
Learn more
04 / Leadership

Fractional CISO Services

Senior security leadership on a part-time, retained basis.

  • Security strategy, roadmap and budget advice
  • Board and leadership reporting; security governance forums
  • Client security questionnaires, contractual security terms and due diligence
Learn more
05 / Risk

Information Security, Risk & Compliance Consulting

Pragmatic advisory across security governance, risk management and regulatory expectations.

  • Information security risk assessments
  • Policy, standards and control framework design
  • Business continuity and incident response planning
Learn more
06 / Quality

ISO 9001 Quality Management Consulting & Auditing

Build, audit and improve a quality management system that supports the business.

  • QMS gap assessment and implementation support
  • Process mapping, objectives and performance indicators
  • Internal audits and management review support
Learn more
07 / Capability

Tailored Training

Practical, engaging training for leadership, auditors and teams.

Build team capability
Security awarenessISO 27001 auditor trainingISO 9001 foundationsRisk-led workshops
Clear-eyed advice.
Practical by design.

Rigour matters. So does making the next step feel possible.

03 Why work with us

Auditor rigour.
Operator experience.

Most advisers have either audited systems or run them. Our principal has done both — on the auditor’s side of the table at large corporates, and on the CISO’s side while defending programmes to demanding clients.

  • Senior-led. You work directly with the principal, not a rotating junior team.
  • Right-sized. Controls and documentation matched to your size and risk.
  • Audit-ready. Evidence and processes designed for how auditors test.
  • Teaching-minded. We build your team’s capability, not dependency.
About the principal
01

Independent

Vendor-neutral advice with no certification body or product to sell.

02

Pragmatic

Security that enables the business rather than slowing it down.

03

Confidential

NDA-backed engagements and disciplined handling of your information.

04

Experienced

25+ years across organisations of all sizes and sectors.

04 How we work

Structured enough
to trust. Flexible enough to fit.

A focused engagement, shaped to your needs and delivered with clear ownership at every step.

  1. 01
    Discover

    Understand the context

    We start with your objectives, current controls, operating model and the realities your teams face.

  2. 02
    Assess

    Find the signal

    A gap assessment or risk review establishes where you are and what matters most.

  3. 03
    Plan

    Agree the path

    A written proposal with scope, timeline, deliverables and fees agreed up front.

  4. 04
    Deliver

    Make progress together

    Hands-on implementation, audit or advisory work with regular progress reporting.

  5. 05
    Sustain

    Keep improving

    Follow-up, training and support so improvements stick through surveillance audits.

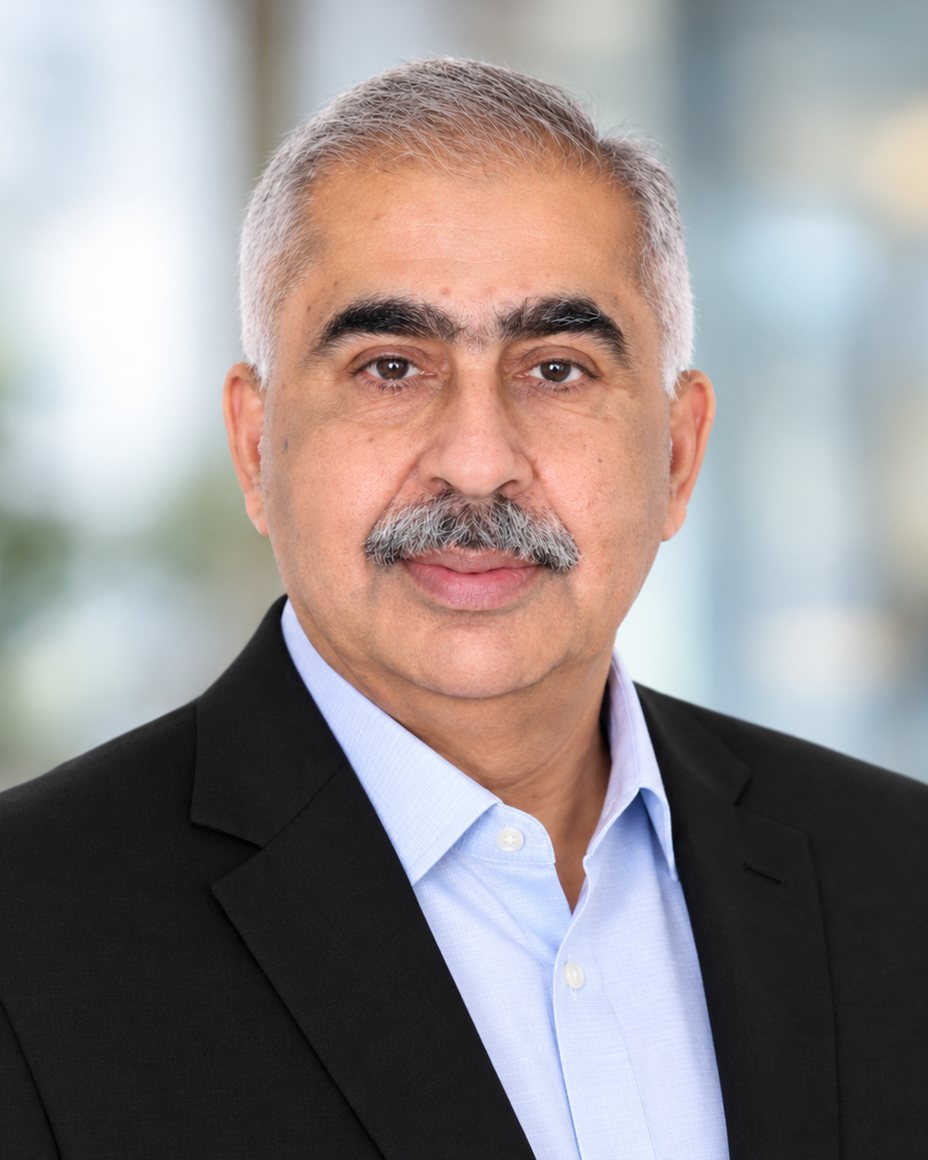
Portrait of Jayant Luthra
25+YEARS OF
EXPERIENCE
05 Who you work with

Experience that
sees the whole picture.

Jayant Luthra is an ISO/IEC 27001 certified information security auditor and ISO 9001 certified auditor with more than 25 years of experience building information security systems for organisations of all sizes.

He has conducted internal and third-party audits at large corporates across India as a consultant auditor engaged with DNV, and has served as CISO for a Chicago-headquartered legal services offshoring firm and a San Francisco-headquartered lead-generation marketing corporation.

ISO/IEC 27001Lead Auditor · DNVISO 9001Lead Auditor · DNVDNVConsultant auditor experience

Independent consulting firm; no claim of certification-body accreditation or DNV endorsement.

Read full profile
06 Good to know

A few things
you may be wondering.

Every organisation is different. Start with a conversation about yours.

Ask us directly
Are you a certification body, and can you certify us?

No. We are an independent consulting firm. Certification to ISO/IEC 27001 or ISO 9001 is issued only by accredited certification bodies. We help you prepare for, and succeed in, that audit.

Is there a conflict of interest if you help us implement and also audit?

We manage this carefully. Where we have helped design a system, we recommend that independent internal audits are performed by a different resource, and we will tell you plainly if an engagement would compromise objectivity.

How long does ISO 27001 readiness take?

It depends on scope, size and current maturity. Many organisations take several months from gap assessment to certification audit. We provide a realistic timeline after an initial scoping discussion.

We are small. Is ISO 27001 overkill?

Not if it is right-sized. Customers increasingly ask for evidence of security controls. We scope the ISMS to what your organisation actually needs and avoid unnecessary bureaucracy.

What is a Fractional CISO engagement like?

A defined monthly commitment covering strategy, governance, customer security assurance and team guidance. The scope and cadence are agreed up front and can scale as you grow.

Do you work with organisations outside India?

Yes. Engagements can be delivered remotely or on-site. Please get in touch with your location and requirements.

Do you offer one-off services?

Yes — a single internal audit, a gap assessment, a supplier audit or a training workshop can all be engaged individually.

How is confidential information handled?

Engagements are covered by a non-disclosure agreement, and we handle client information in line with the same information security practices we advise on.

07 Let’s talk

Make your next step
a confident one.

Tell us what you are working towards. We’ll respond within two business days to arrange an initial conversation.

LOCATION

Pune, India

Initial enquiry* Required

Your details are used only to respond to your enquiry. See our privacy policy.